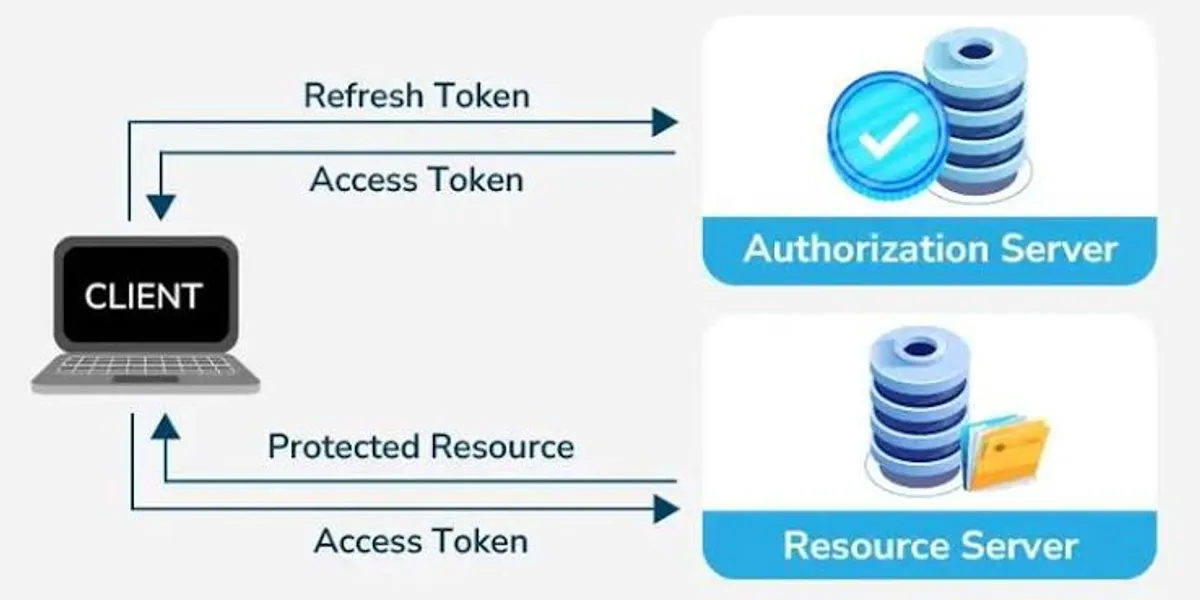
A single long-lived JWT can't be both secure and convenient. Splitting it into a short-lived access token and a rotating, revocable refresh token is what makes logout, role changes, and theft detection possible at all.
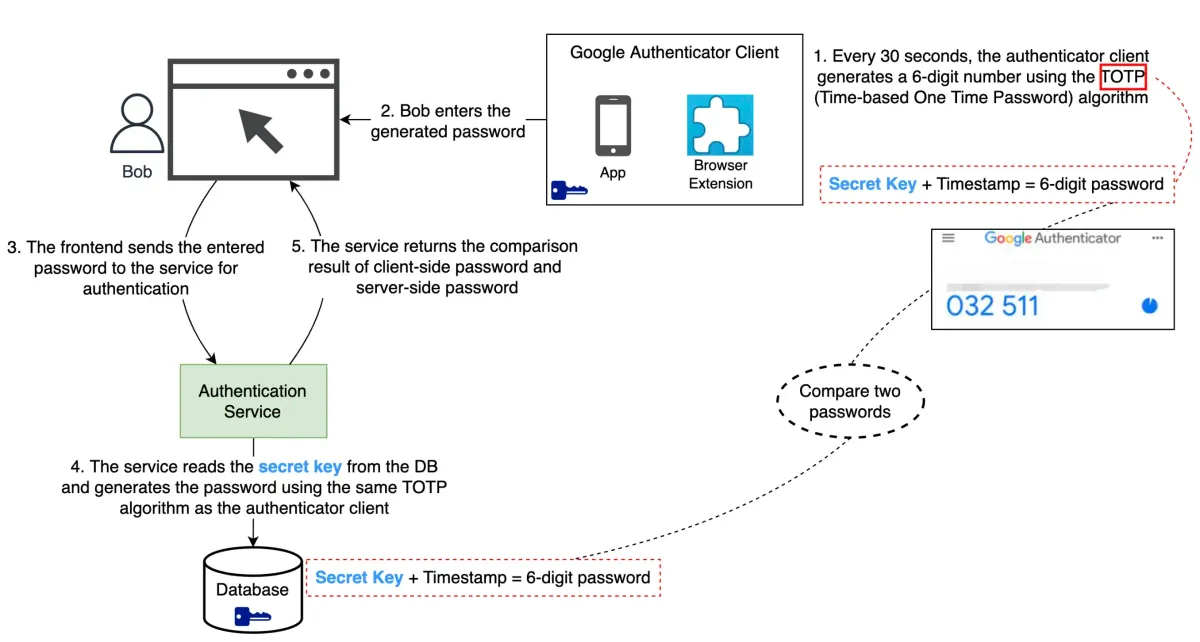
A developer-focused explanation of authenticator apps, TOTP (RFC 6238), otpauth URIs, time drift handling, and the security properties behind offline 2FA codes.